
Merchant onboarding is the multi-stage workflow that turns a business application into a live, risk-profiled merchant account ready to accept payments. It runs through prescreening, KYC/KYB verification, underwriting, technical integration, and ongoing monitoring, guided by standards like FinCEN's CDD rule and PCI SSC payment-page rules. Success means a merchant processing transactions within set limits, under active monitoring, with providers like Paysec supporting the setup.
TL;DR:
- Prescreening verifies business registration, website accuracy, and prohibited goods, reducing application delays and focusing compliance efforts effectively.
- Mandatory documents include articles of incorporation, EIN confirmation, government IDs, and industry licenses; beneficial owners must be verified at 25% control per FinCEN rules.
- Automated identity checks and registry lookups handle most straightforward verification cases, while manual review remains for complex or unusual structures.
- Underwriting assesses industry risk, chargeback history, and transaction types to determine limits and ongoing monitoring, with re-verification triggered by significant business changes.
- Continuous risk management, transparency, and industry-specific underwriting are key to successful onboarding and long-term merchant compliance and profitability.
Table of Contents
- What Is the Merchant Onboarding Process, Step by Step?
- How Does Prescreening Reduce Onboarding Friction?
- What Documents Do You Need for Merchant KYC and KYB?
- How Does Underwriting Decide Merchant Risk and Limits?
- What Should a Technical Integration Checklist Cover?
- What PCI Compliance Rules Apply During Onboarding?
- What Happens During Activation and the First Days Live?
- How Often Should Merchants Be Re-Verified After Onboarding?
- What Are the Biggest Onboarding Challenges and How Do You Fix Them?
- How Does Paysec Support Merchant Onboarding?
- Onboarding Is a Risk Program, Not a Paperwork Checklist
- Start Onboarding With Paysec
- Sources
- FAQ
What Is the Merchant Onboarding Process, Step by Step?
The sequence runs through five distinct phases, each owned by a different team. A merchant submits an application and documents. Compliance staff run KYC/KYB checks and screen beneficial owners. Underwriters score risk and set processing limits. A technical team handles gateway or terminal integration and test transactions. Finally, the acquirer or payment service provider activates the account and starts continuous monitoring.
Timelines vary sharply by how much of this is automated. Traditional acquirer workflows built on manual phone and email checks commonly take 3 to 7 days to complete, largely because staff are chasing paperwork and re-keying data by hand. Automated platforms that use identity verification APIs and AI-driven fraud scoring compress that window considerably, often producing same-day or next-day decisions for straightforward applications.
Before a merchant reaches underwriting, they typically need to have these documents ready:
- Business formation documents (articles of incorporation or organization)
- Employer Identification Number (EIN) confirmation
- Voided check or bank letter for the settlement account
- Government-issued ID for each principal and beneficial owner
- Industry-specific licenses where applicable (liquor, cannabis-adjacent, lending)
- Processing history or bank statements for existing businesses
Missing even one of these items is the single biggest cause of stalled applications, which is why the prescreen stage matters so much.
How Does Prescreening Reduce Onboarding Friction?
Prescreening is a light-touch review that happens before a merchant fills out a full application. It exists to catch obvious mismatches early, before compliance staff invest time on a file that was never going to pass underwriting. Skipping this step is how teams end up with a pile of half-finished applications and frustrated business owners.
A solid prescreen checks three things in order:
- Business existence. Confirm the entity is registered with the relevant state, has an active status, and the name on the application matches public filings.
- Website and storefront match. For e-commerce merchants, the site should reflect the products or services described in the application, with working checkout, contact information, and clear return or refund terms.
- Prohibited or restricted goods screening. Flag anything touching firearms, adult content, unregulated pharmaceuticals, or other categories the acquiring bank restricts, and route it to specialized underwriting instead of a standard queue.
Clear communication at this stage prevents most downstream delays. A document checklist with real examples, sample formats, and an upload portal that shows progress in real time cuts back-and-forth emails dramatically. Merchants abandon applications far more often when they are asked to guess what a "acceptable bank letter" looks like than when they are shown one.
Red flags at prescreen do not automatically mean rejection. A mismatched business name might just be a DBA that was not filed with the state. A website under construction might mean the merchant is pre-launch and needs a provisional review instead of a hard decline. Triage each flag by severity: hard stops (prohibited products, sanctioned entities) get an immediate decline, while soft flags (incomplete site, minor name mismatch) get routed to a specialist for a quick follow-up call.
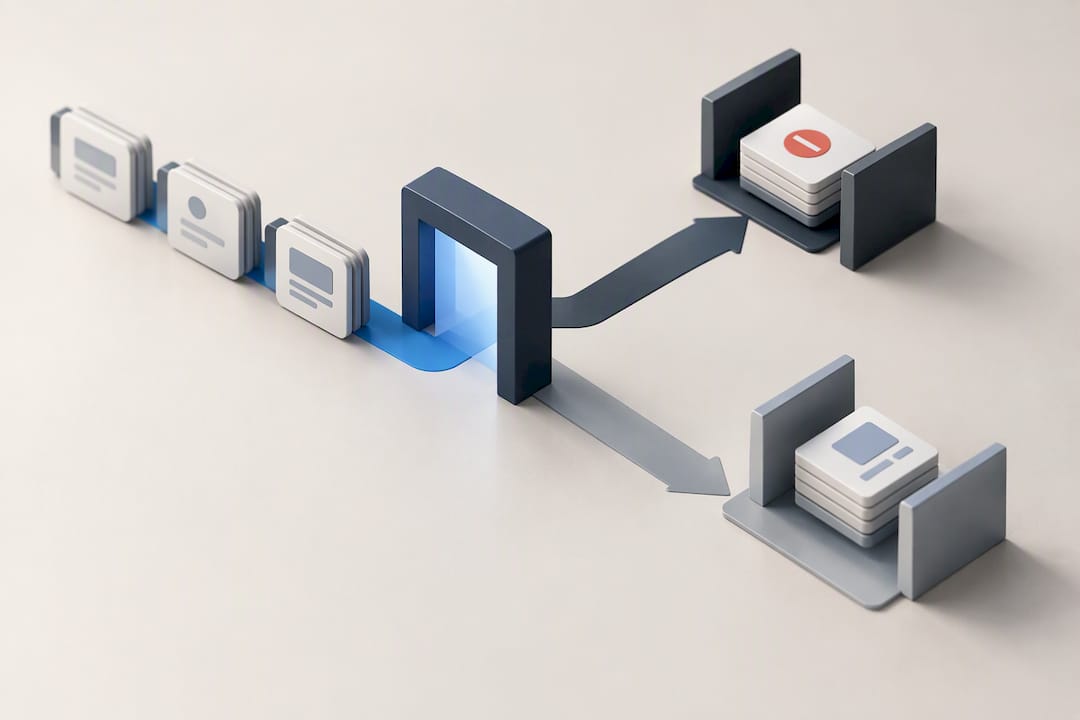
Pro Tip: Build your prescreen checklist as a shared document with real screenshots of acceptable and unacceptable submissions. Merchants copy what they can see far more accurately than what they are told.
What Documents Do You Need for Merchant KYC and KYB?
Verifying a business and the people behind it is where onboarding stops being a formality and starts being regulatory work. The standard document set includes articles of incorporation, an EIN letter from the IRS, a bank account confirmation, and government-issued identification for every principal and beneficial owner. Regulated industries add licenses: a liquor license for a bar, a money transmitter license for certain fintech merchants, or state cannabis-adjacent registrations where relevant.
Beneficial ownership verification follows FinCEN's Customer Due Diligence rule, which requires covered institutions to identify and verify individuals who own or control 25% or more of a business at account opening. That threshold applies regardless of industry, and FinCEN provides limited relief on re-verification only in specific, defined situations, so most onboarding teams re-check ownership whenever a material change is reported rather than on a fixed calendar. The Corporate Transparency Act's beneficial ownership information reporting requirements add another layer, since many merchants now file BOI reports directly with FinCEN, and that filed data can sometimes be cross-referenced during onboarding.
Verification methods split into a few practical categories:
- Automated identity checks: document scanning combined with liveness or selfie matching for principals and owners
- Registry lookups: direct queries against state Secretary of State databases to confirm entity status and registered agents
- Certified document review: manual review of articles, licenses, and bank letters when automated matching fails or the entity structure is unusual (trusts, multi-layer holding companies)
Automated identity verification handles the majority of straightforward cases, freeing compliance staff to focus on files that genuinely need judgment.
How Does Underwriting Decide Merchant Risk and Limits?
Underwriting turns a verified application into an actual risk profile. That profile determines how much monitoring a merchant gets and where the processing limits sit, and it should keep evolving after go-live rather than freezing at approval. FFIEC guidance frames due diligence as an ongoing exercise precisely because a merchant's risk today is not necessarily its risk in six months.
The main risk drivers underwriters weigh include:
- Industry category (subscription SaaS looks very different from CBD retail or high-ticket travel)
- Chargeback ratios and dispute history, either from prior processing statements or industry benchmarks
- Transaction mix, especially the split between card-present and card-not-present volume
- Prior processing history, including any terminated merchant file (MATCH/TMF) hits
Outcomes from underwriting are not simply "approved" or "declined." Common results include:
- Rolling reserves, where a percentage of daily volume is held back for a set period to cover potential chargebacks
- Capped transaction limits, which raise automatically as the merchant builds a clean processing history
- Temporary holds on payouts pending supplemental documentation
Supplemental proof gets requested when the standard file leaves a gap: recent bank statements to confirm cash flow, proof of fulfillment for high-ticket or pre-order goods, or license verification for regulated categories. Acquirers retain ultimate responsibility for this due diligence even when an ISO or processor handles day-to-day onboarding, which is why premises checks and website reviews stay standard practice for e-commerce merchants.
Pro Tip: If a merchant's chargeback history looks borderline, ask for the last three months of processing statements before declining outright. A single bad month tied to a shipping delay reads very differently from a sustained pattern.
Merchants in categories like high-risk retail benefit from underwriting teams that understand the vertical instead of applying a generic scorecard.
What Should a Technical Integration Checklist Cover?
Getting a merchant live technically is a separate job from getting them approved on paper, and rushing it is how declines and reconciliation headaches show up in week one. The right checklist depends on how the merchant plans to accept payments.
- Pick the integration mode and confirm required fields. Hosted checkout needs branding assets and redirect URLs; a direct API integration needs API keys, webhook endpoints, and a sandbox environment; a physical terminal needs provisioning, network configuration, and a test card run.
- Run sandbox transactions before touching production. Test a full authorization, a partial refund, a voided transaction, and a declined card to confirm every response code is handled correctly on the merchant's side.
- Verify webhooks fire and are acknowledged. A payment can succeed on the processor's end and still fail silently for the merchant if a webhook listener is misconfigured or timing out.
- Confirm settlement and reconciliation. Run at least one full settlement cycle and match the deposited amount against the transaction report line by line before calling integration complete.
- Check for common preflight errors. Mismatched currency codes, missing address verification fields, and expired sandbox credentials cause the majority of post-launch decline spikes.
A merchant switching from a legacy processor should treat this checklist as mandatory even if their old integration "worked fine," since gateway-specific field requirements rarely map one to one. The eCommerce merchant account setup guide walks through the online-specific version of this process in more detail.
What PCI Compliance Rules Apply During Onboarding?
Merchants routinely assume that using a payment service provider automatically makes them PCI compliant. It does not. A merchant still has to attest to the correct Self-Assessment Questionnaire for its business model, and if it outsources payment capture to a third-party service provider (TPSP), it still has to confirm and document that provider's own compliance status rather than assume it. PCI's small merchant guidance is explicit that outsourcing reduces scope but never eliminates the merchant's own responsibility.
For e-commerce specifically, the compliance bar moved in 2025. PCI SSC issued guidance targeting e-skimming, the practice of injecting malicious code into a checkout page to steal card data in real time. Requirements 6.4.3 and 11.6.1 became effective after March 31, 2025, and they call for payment page integrity checks and mechanisms to detect unauthorized script changes.
By the numbers: PCI's own information supplement frames e-skimming controls as a direct response to attacks that historically bypassed traditional network firewalls entirely, since the malicious script runs inside the customer's browser on a page that already passed a standard vulnerability scan.
Practical controls to build into onboarding evidence include:
- Payment page integrity monitoring or a change-detection tool for checkout scripts
- Regular Approved Scanning Vendor (ASV) scans for any merchant with a public-facing payment page
- HTTP header controls (Content Security Policy) that restrict which scripts can load on checkout pages
- Signed attestations from any TPSP confirming their own PCI scope
Onboarding teams should capture SAQ type, ASV scan reports, and TPSP attestations as part of the file itself, not as a follow-up task after go-live. Paysec's security and encryption approach reflects this same principle: compliance evidence gets documented at the point of setup, not retrofitted later.
What Happens During Activation and the First Days Live?
Activation is the handoff moment where a fully underwritten, technically tested merchant actually starts moving real money. Rushing this stage is where avoidable support tickets come from.
- Collect final signatures on the merchant agreement and pricing terms.
- Verify the payout bank account with a micro-deposit or instant verification method before the first real settlement.
- Provision terminals or confirm gateway credentials are switched from sandbox to production.
- Process one live test settlement at a small dollar amount to confirm funds actually land correctly.
- Deliver a short training session covering how to issue a refund, respond to a dispute notice, and read a daily reconciliation report.
Merchant training does not need to be lengthy, but skipping it guarantees a support call within the first week. The three things merchants ask about most in year one are refunds, chargeback response deadlines, and why a settlement amount does not exactly match gross sales (fees and reserves explain nearly all of that gap).
The first 24 to 72 hours after go-live deserve active attention rather than a "set it and forget it" assumption. Watch for authorization failure spikes, unusually high average ticket sizes compared to the application, and any refund pattern that looks automated rather than customer-driven.
How Often Should Merchants Be Re-Verified After Onboarding?
Onboarding does not end at activation. FFIEC guidance treats due diligence as continuous, meaning the risk profile built at approval should update whenever something material changes, not just at a fixed annual review date.
Specific triggers that should prompt re-verification include:
- A sudden chargeback ratio spike beyond the merchant's historical baseline
- A processing volume surge well beyond the limits set at underwriting
- Regulatory alerts or sanctions list matches on a beneficial owner
- A change in beneficial ownership structure reported by the merchant or discovered through monitoring
Review cadence should scale with risk tier. Low-risk merchants with clean histories might get a light annual check. Higher-risk categories, or any merchant that hit a trigger event, warrant quarterly or even monthly review until the pattern stabilizes.
When something does trip a trigger, the response should be proportionate. A modest volume increase might just need an updated bank statement. A serious chargeback spike might justify a temporary reserve increase or a short processing hold while the merchant explains the cause. Enhanced monitoring, rather than an automatic termination, is usually the right first move for a merchant with a genuine track record.
What Are the Biggest Onboarding Challenges and How Do You Fix Them?
Most onboarding delays trace back to a small number of repeatable causes, and most of them have straightforward operational fixes.
- Incomplete documentation is the top delay cause. Fix it with a visual checklist showing acceptable document examples before the merchant even starts the application.
- Unclear application status drives merchants to call or email repeatedly. A self-serve portal showing real-time progress cuts that volume significantly.
- Manual re-keying of data between systems introduces errors and slows underwriting. Automated data capture at intake removes most of this.
- Vague rejection reasons push good merchants to abandon rather than fix the issue. Specific, actionable rejection messages ("bank letter must show account number and routing number") recover applications that a generic denial would lose.
Track average time-to-approval, application abandonment rate, and percentage of files requiring supplemental documents as your core onboarding health metrics.
Pro Tip: If your abandonment rate spikes at one specific step in the portal, that step is almost always the actual problem, even if merchants complain about something else entirely.
How Does Paysec Support Merchant Onboarding?
Paysec structures onboarding around transparent pricing and dedicated support rather than a one-size-fits-all approval queue. Merchants get access to a range of tools built for the operational realities covered above:
- Network Offset Pricing that passes through true wholesale interchange rates, so merchants see exactly what they are paying instead of a flat markup
- Merchant services covering in-store processing, eCommerce gateway integration, mobile payments, and recurring billing under one account
- Enhanced data optimization for B2B merchants looking to reduce interchange costs on commercial card transactions
- Fraud prevention tools built into the onboarding and integration process rather than bolted on afterward
- Support for high-risk and specialized verticals, including CBD retail and healthcare, where standard underwriting scorecards fall short
Merchants in various sectors experience notable savings on processing costs compared to traditional flat-rate processors. Detailed transaction reporting gives merchants ongoing visibility into fees and settlement, which matters as much after onboarding as it does during the application itself.
Onboarding Is a Risk Program, Not a Paperwork Checklist
The businesses that get onboarding right treat it as continuous risk management, not a gate you pass once and forget. Every underwriting decision, every re-verification trigger, every PCI attestation exists to keep a merchant's risk profile accurate as their business actually changes. Teams that bolt compliance on after the fact, rather than building it into the application flow itself, end up doing the same work twice.
Paysec's priorities reflect that mindset: transparent, interchange-based pricing instead of hidden markups, dedicated merchant services rather than a generic support queue, and industry-specific underwriting for categories that get rejected elsewhere. Good onboarding is judged by what happens in month six, not just how fast the first approval came through.
— PaySec Marketing Team
Start Onboarding With Paysec
Network Offset Pricing offers merchants an alternative to flat-rate processors and hidden interchange markups by providing direct visibility into wholesale rates, without long-term contracts or minimums.
Getting started is straightforward: review the pricing structure to compare Network Offset, Flat Rate, and Custom Enterprise options, or browse merchant services to see how in-store processing, eCommerce gateways, and recurring billing fit your setup. Businesses that want a terminal without upfront hardware costs can look at the Free Placement program as a starting point. High-volume merchants or those with complex vertical requirements can request custom enterprise pricing directly. After reaching out, expect a walkthrough of your specific processing needs and a straightforward path to a live merchant account, backed by detailed transaction reporting from day one.
Sources
- Mastercard: Digital merchant onboarding insights
- FinCEN: CDD Rule FAQs
- FFIEC: Assessing compliance with BSA regulatory requirements
- PCI SSC: Payment page security and preventing e-skimming (information supplement)
- FFIEC IT Handbook: Merchant acquiring
FAQ
How Long Does the Merchant Onboarding Process Take?
Manual, phone-and-email based onboarding commonly takes 3 to 7 days, while automated platforms using identity verification and AI-driven risk scoring can approve straightforward applications much faster. Complex or high-risk merchants take longer due to supplemental document requests.
What Documents Are Required for Merchant Onboarding?
Standard requirements include articles of incorporation, an EIN confirmation, a bank account letter, government ID for principals and beneficial owners, and any industry-specific licenses. Beneficial owners holding 25% or more of the business must be identified and verified under FinCEN's CDD rule.
Who Is Responsible for PCI Compliance During Onboarding?
Both the merchant and the payment service provider share responsibility. Merchants must complete the correct Self-Assessment Questionnaire and confirm any third-party service provider's PCI scope through a signed attestation rather than assuming compliance by default.
What Triggers a Merchant Re-Verification After Approval?
Common triggers include a chargeback ratio spike, a sudden transaction volume surge, a regulatory or sanctions alert, or a change in beneficial ownership. FFIEC guidance treats onboarding due diligence as continuous rather than a one-time event.
Does Paysec Charge for Onboarding Setup?
Paysec's Free Placement program is available at $0 per month for eligible terminal setups, while Network Offset, Flat Rate, and Custom Enterprise pricing details are available directly on the pricing page.